we provide Refined Fortinet NSE7_EFW-6.2 exam answers which are the best for clearing NSE7_EFW-6.2 test, and to get certified by Fortinet Fortinet NSE 7 - Enterprise Firewall 6.2. The NSE7_EFW-6.2 Questions & Answers covers all the knowledge points of the real NSE7_EFW-6.2 exam. Crack your Fortinet NSE7_EFW-6.2 Exam with latest dumps, guaranteed!
Free NSE7_EFW-6.2 Demo Online For Fortinet Certifitcation:
NEW QUESTION 1
View the IPS exit log, and then answer the question below.
# diagnose test application ipsmonitor 3 ipsengine exit log”
pid = 93 (cfg), duration = 5605322 (s) at Wed Apr 19 09:57:26 2021 code = 11, reason: manual
What is the status of IPS on this FortiGate?
- A. IPS engine memory consumption has exceeded the model-specific predefined value.
- B. IPS daemon experienced a crash.
- C. There are communication problems between the IPS engine and the management database.
- D. All IPS-related features have been disabled in FortiGate’s configuration.
Answer: D
Explanation:
The command diagnose test application ipsmonitor includes many options that are useful for troubleshooting purposes.Option 3 displays the log entries generated every time an IPS engine process stopped. There are various reasons why these logs are generated:Manual: Because of the configuration, IPS no longer needs to run (that is, all IPS-releated features have been disabled)
NEW QUESTION 2
View the exhibit, which contains the output of diagnose sys session stat, and then answer the question below.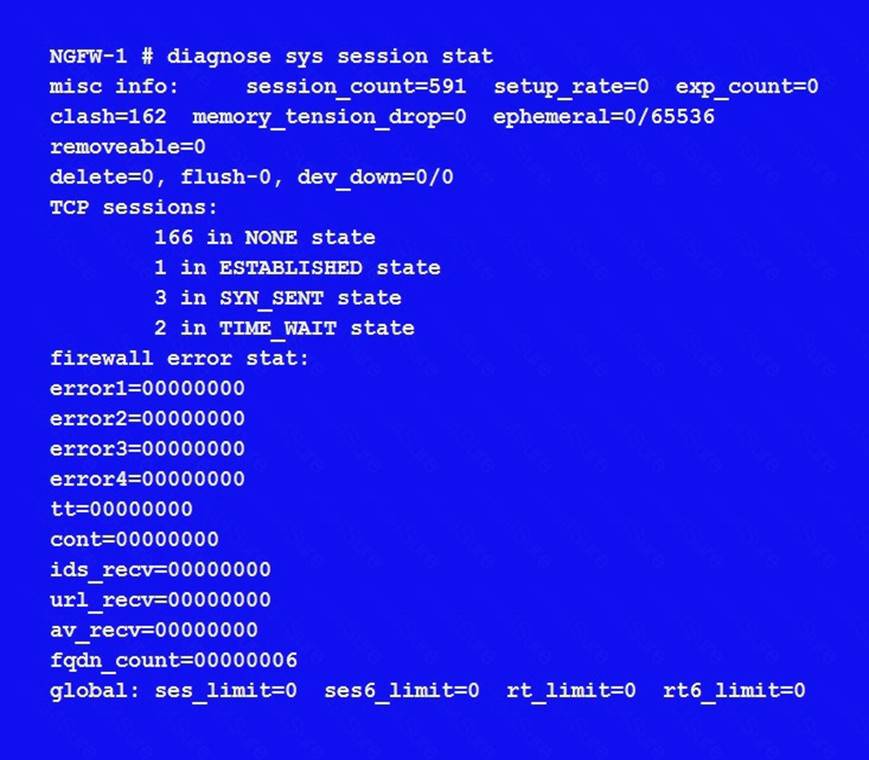
Which statements are correct regarding the output shown? (Choose two.)
- A. There are 0 ephemeral sessions.
- B. All the sessions in the session table are TCP sessions.
- C. No sessions have been deleted because of memory pages exhaustion.
- D. There are 166 TCP sessions waiting to complete the three-way handshake.
Answer: AC
Explanation:
https://kb.fortinet.com/kb/documentLink.do?externalID=FD40578
NEW QUESTION 3
Examine the following partial output from two system debug commands; then answer the question below.

Which of the following statements are true regarding the above outputs? (Choose two.)
- A. The unit is running a 32-bit FortiOS
- B. The unit is in kernel conserve mode
- C. The Cached value is always the Active value plus the Inactive value
- D. Kernel indirectly accesses the low memory (LowTotal) through memory paging
Answer: AC
NEW QUESTION 4
What configuration changes can reduce the memory utilization in aFortiGate? (Choose two.)
- A. Reduce the session time to live.
- B. Increase the TCP session timers.
- C. Increase the FortiGuard cache time to live.
- D. Reduce the maximum file size to inspect.
Answer: AD
NEW QUESTION 5
Examine the following routing table and BGP configuration; then answer the question below.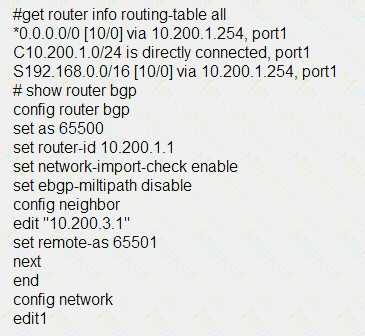
TheBGP connection is up, but the local peer is NOT advertising the prefix 192.168.1.0/24. Which configuration change will make the local peer advertise this prefix?
- A. Enable the redistribution of connected routers into BGP.
- B. Enable the redistribution of static routers into BGP.
- C. Disable the setting network-import-check.
- D. Enable the setting ebgp-multipath.
Answer: C
NEW QUESTION 6
Examine the partial output from two web filter debug commands; then answer the question below:
Based on the above outputs, which is the FortiGuard web filter category for the web site www.fgt99.com?
- A. Finance and banking
- B. General organization.
- C. Business.
- D. Information technology.
Answer: C
NEW QUESTION 7
A FortiGate is rebooting unexpectedly without any apparent reason. What troubleshooting tools could an administrator use to get more information about the problem? (Choose two.)
- A. Firewall monitor.
- B. Policy monitor.
- C. Logs.
- D. Crashlogs.
Answer: CD
NEW QUESTION 8
View these partial outputs from two routing debug commands: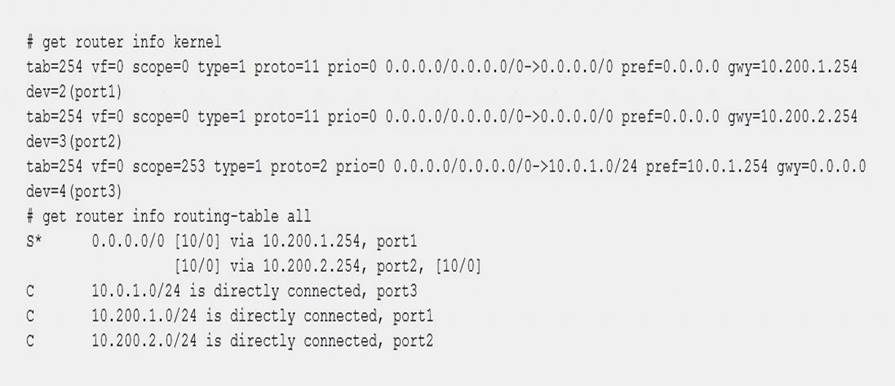
Which outbound interface will FortiGate use to route web traffic from internal users to the Internet?
- A. Both port1 and port2
- B. port3
- C. port1
- D. port2
Answer: A
NEW QUESTION 9
What conditions are required for two FortiGate devices to form an OSPF adjacency? (Choose three.)
- A. IP addresses are in the same subnet.
- B. Helloand dead intervals match.
- C. OSPF IP MTUs match.
- D. OSPF peer IDs match.
- E. OSPF costs match.
Answer: ABC
Explanation:
https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-advanced-routing-54/Routing_OSPF/OSPF_Bac
NEW QUESTION 10
View the exhibit, which contains a screenshot of some phase-1 settings, and then answer the question below.
The VPN is up, and DPD packets are being exchanged between both IPsec gateways; however, traffic cannot pass through the tunnel. To diagnose, the administrator enters these CLI commands: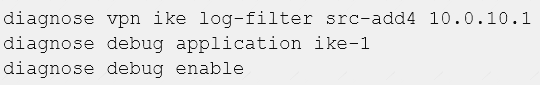
However, the IKE real time debug does not show any output. Why?
- A. The debug output shows phases 1 and 2 negotiations onl
- B. Once the tunnel is up, it does not show any more output.
- C. The log-filter setting was setincorrectl
- D. The VPN’s traffic does not match this filter.
- E. The debug shows only error message
- F. If there is no output, then the tunnel is operating normally.
- G. The debug output shows phase 1 negotiation onl
- H. After that, the administrator must enable the following real time debug: diagnose debug application ipsec -1.
Answer: D
NEW QUESTION 11
The logs in a FSSO collector agent (CA) are showing the following error: failed to connect to registry: PIKA1026 (192.168.12.232)
What can be the reason for this error?
- A. The CA cannot resolve the name of the workstation.
- B. The FortiGate cannot resolve the name of the workstation.
- C. The remote registry service is not running in the workstation 192.168.12.232.
- D. The CA cannot reach the FortiGate with the IP address 192.168.12.232.
Answer: C
Explanation:
https://kb.fortinet.com/kb/documentLink.do?externalID=FD30548
NEW QUESTION 12
Which statements about bulk configuration changes using FortiManager CLI scripts are correct? (Choose two.)
- A. When executed on the Policy Package,ADOM database, changes are applied directly to the managed FortiGate.
- B. When executed on the Device Database, you must use the installation wizard to apply the changes to the managed FortiGate.
- C. When executed on the All FortiGate in ADOM, changes are automatically installed without creating a new revision history.
- D. When executed on the Remote FortiGate directly, administrators do not have the option to review the changes prior to installation.
Answer: BD
Explanation:
CLI scripts can be run in threedifferent ways:Device Database: By default, a script is executed on the device database. It is recommend you run the changes on the device database (default setting), as this allows you to check what configuration changes you will send to the managed device. Once scripts are run on the device database, you can install these changes to a managed device using the installation wizard.
Policy Package, ADOM database: If a script contains changes related to ADOM level objects and policies, you can change the default selection to run on Policy Package, ADOM database and can then be installed using the installation wizard.
Remote FortiGate directly (through CLI): A script can be executed directly on the device and you don’t need to install these changes using theinstallation wizard. As the changes are directly installed on the managed device, no option is provided to verify and check the configuration changes through FortiManager prior to executing it.
NEW QUESTION 13
An LDAP user cannot authenticate against a FortiGate device. Examine the real time debug output shown in the exhibit when the user attempted the authentication; then answer thequestion below.

Based on the output in the exhibit, what can cause this authentication problem?
- A. User student is not found in the LDAP server.
- B. User student is using a wrong password.
- C. The FortiGate has been configured with the wrong password for the LDAP administrator.
- D. The FortiGate has been configured with the wrong authentication schema.
Answer: A
NEW QUESTION 14
The CLI command set intelligent-mode <enable | disable> controls the IPS engine’s adaptive scanning behavior. Which of the following statements describes IPS adaptive scanning?
- A. Determines the optimal number of IPS engines required based on system load.
- B. Downloads signatures on demand from FDS based on scanning requirements.
- C. Determines when it is secure enough to stop scanning session traffic.
- D. Choose a matching algorithm based on available memory and the type of inspection being performed.
Answer: C
Explanation:
Configuring IPS intelligenceStarting with FortiOS 5.2, intelligent-mode is a new adaptive detection method. This command is enabled the default and it means that the IPS engine will perform adaptive scanning so that, for some traffic, the FortiGate can quickly finish scanning and offload the traffic to NPU or kernel. It is a balanced method which could cover all known exploits. When disabled, the IPS engine scans every single byte.
config ips globalset intelligent-mode {enable|disable}end
NEW QUESTION 15
Examine the following partial outputs from two routing debug commands; then answer the question below.
# get router info kernel
tab=254 vf=0 scope=0type=1 proto=11 prio=00.0.0.0/0.0.0.0/0->0.0.0.0/0 pref=0.0.0.0 gwy=10.200.1.254 dev=2(port1)
tab=254 vf=0 scope=0type=1 proto=11 prio=10 0.0.0.0/0.0.0.0/0->0.0.0.0/0 pref=0.0.0.0 gwy=10.200.2.254 dev=3(port2)
tab=254 vf=0 scope=253type=1 proto=2 prio=0 0.0.0.0/0.0.0.0/.->10.0.1.0/24 pref=10.0.1.254 gwy=0.0.0.0 dev=4(port3)
# get router info routing-table all s*0.0.0.0/0 [10/0] via 10.200.1.254, portl [10/0] via 10.200.2.254, port2, [10/0] dO.0.1.0/24 is directly connected, port3 dO.200.1.0/24 is directly connected, portl d0.200.2.0/24 is directly connected, port2
Which outbound interface or interfaces will be used by this FortiGate to route web traffic from internal users to the Internet?
- A. port!
- B. port2.
- C. Both portl and port2.
- D. port3.
Answer: B
NEW QUESTION 16
View the exhibit, which contains the output of a BGP debug command, and then answer the question below.
Which of the following statements about the exhibit are true? (Choose two.)
- A. For the peer10.125.0.60, the BGP state of is Established.
- B. The local BGP peer has received a total of three BGP prefixes.
- C. Since the BGP counters were last reset, the BGP peer 10.200.3.1 has never been down.
- D. The local BGP peer has not established a TCP sessionto the BGP peer 10.200.3.1.
Answer: AD
NEW QUESTION 17
An administrator has configured the following CLI script on FortiManager, which failed to apply any changes to the managed device afterbeing executed.
Why didn’t the script make any changes to the managed device?
- A. Commands that start with the # sign are not executed.
- B. CLI scripts will add objects only if they are referenced by policies.
- C. Incomplete commands are ignored in CLI scripts.
- D. Static routes can only be added using TCL scripts.
Answer: A
Explanation:
https://help.fortinet.com/fmgr/50hlp/56/5-6-2/FortiManager_Admin_Guide/1000_Device%20Manager/2400_Sc
A sequence of FortiGate CLI commands, as you would type them at the command line.A comment line starts with the number sign (#). A comment line will not be executed.
NEW QUESTION 18
How does FortiManager handle FortiGuard requests from FortiGate devices, when it is configured as a local FDS?
- A. FortiManager can download and maintain local copies of FortiGuard databases.
- B. FortiManager supports only FortiGuard push to managed devices.
- C. FortiManager will respond to update requests only if they originate from a managed device.
- D. FortiManager does not support rating requests.
Answer: A
NEW QUESTION 19
Examine the following traffic log; then answer the question below.
date-20xx-02-01 time=19:52:01 devname=master device_id="xxxxxxx" log_id=0100020007 type=event subtype=system pri critical vd=root service=kemel status=failure msg="NAT port is exhausted."
What does the log mean?
- A. There is not enough available memory in the system to create a new entry in the NAT port table.
- B. The limit for the maximum number of simultaneous sessions sharing the same NAT port has been reached.
- C. FortiGate does not have any available NAT port for a new connection.
- D. The limit for the maximum number of entries in the NAT port table has been reached.
Answer: B
NEW QUESTION 20
Examine the output of the 'diagnose debug rating' command shown in the exhibit; then answer the question below.
Whichstatement are true regarding the output in the exhibit? (Choose two.)
- A. There are three FortiGuard servers that are not responding to the queries sent by the FortiGate.
- B. The TZ value represents the delta between each FortiGuard server's timezone and the FortiGate's time zone.
- C. FortiGate will send the FortiGuard queries to the server with highest weight.
- D. A server's round trip delay (RTT) is not used to calculate its weight.
Answer: BC
NEW QUESTION 21
View the exhibit, which contains a partial web filter profile configuration, and then answer the question below.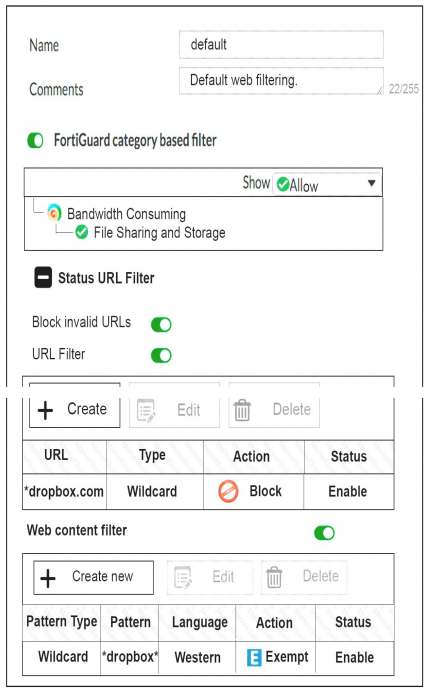
Which action will FortiGate take ifa user attempts to access www.dropbox.com, which is categorized as File Sharing and Storage?
- A. FortiGate will exempt the connection based on the Web Content Filter configuration.
- B. FortiGate will block the connection based on the URL Filterconfiguration.
- C. FortiGate will allow the connection based on the FortiGuard category based filter configuration.
- D. FortiGate will block the connection as an invalid URL.
Answer: B
Explanation:
fortigate does it in order Static URL -> FortiGuard – > Content -> Advanced (java, cookie removal..)so block it in first step
NEW QUESTION 22
An administrator has configured a FortiGate device with two VDOMs: root and internal. The administrator has also created and inter-VDOM link that connects both VDOMs. The objective is to have each VDOM advertise some routes to the other VDOM via OSPF through the inter-VDOM link. What OSPF configuration settings must match in both VDOMs to have the OSPF adjacency successfully forming? (Choose three.)
- A. Router ID.
- B. OSPF interface area.
- C. OSPF interface cost.
- D. OSPF interface MTU.
- E. Interface subnet mask.
Answer: BDE
NEW QUESTION 23
Which two tasks are automated using theInstall Wizard on FortiManager? (Choose two.)
- A. Preview pending configuration changes for managed devices.
- B. Add devices to FortiManager.
- C. Import policy packages from managed devices.
- D. Install configuration changes to managed devices.
- E. Import interface mappings from managed devices.
Answer: AD
Explanation:
https://help.fortinet.com/fmgr/50hlp/56/5-6-2/FortiManager_Admin_Guide/1000_Device%20Manager/1200_ins
There are 4 main wizards:Add Device: is used to add devices to central management and import their configurations.
Install: is used to install configuration changes from Device Manager or Policies & Objects to the managed devices. It allows you to preview the changes and, if the administrator doesn’t agree with the changes, cancel and modify them.
Import policy: isused to import interface mapping, policy database, and objects associated with the managed devices into a policy package under the Policy & Object tab. It runs with the Add Device wizard by default and may be run at any time from the managed device list.
Re-install policy: is used to perform a quick install of the policy package. It doesn’t give the ability to preview the changes that will be installed to the managed device.
NEW QUESTION 24
An administrator has enabled HA session synchronization in a HA cluster with two members. Which flag is added to a primary unit’s session to indicate that it has been synchronized to the secondary unit?
- A. redir.
- B. dirty.
- C. synced
- D. nds.
Answer: C
Explanation:
The synced sessions have the‘synced’ flag. The command ‘diag sys session list’ can be used to see the sessions on the member, with the associated flags.
NEW QUESTION 25
......
Thanks for reading the newest NSE7_EFW-6.2 exam dumps! We recommend you to try the PREMIUM Thedumpscentre.com NSE7_EFW-6.2 dumps in VCE and PDF here: https://www.thedumpscentre.com/NSE7_EFW-6.2-dumps/ (91 Q&As Dumps)