Act now and download your GIAC GPEN test today! Do not waste time for the worthless GIAC GPEN tutorials. Download Most recent GIAC GIAC Certified Penetration Tester exam with real questions and answers and begin to learn GIAC GPEN with a classic professional.
Free demo questions for GIAC GPEN Exam Dumps Below:
NEW QUESTION 1
You want to retrieve password files (stored in the Web server's index directory) from various Web sites. Which of the following tools can you use to accomplish the task?
- A. Sam spade
- B. Nmap
- C. Whois
- D. Google
Answer: D
NEW QUESTION 2
What is the purpose of die following command:
nc.exe -I -p 2222 -e cmd.exe
- A. It is used to start a persistent listener linked to cmd.exe on port 2222 TCP
- B. It is used to start a listener linked to cmd.exe on port 2222 TCP
- C. It is used to start a listener linked to cmd.exe on port 2222 UDP
- D. It is used to start a persistent listener linked to cmd.exe on port 2222 UDP
Answer: C
NEW QUESTION 3
Which of the following best describes a server side exploit?
- A. Attack on the physical machine
- B. Attack of a service listening on a network port
- C. Attack that escalates user privilege to root or administrator
- D. Attack of a client application that retrieves content from the network
Answer: C
NEW QUESTION 4
Which of the following ports must you filter to check null sessions on your network?
- A. 139 and 445
- B. 111 and 222
- C. 1234 and 300
- D. 130 and 200
Answer: A
NEW QUESTION 5
John works as a professional Ethical Hacker. He has been assigned the project of testing the security of www.we-are-secure.com. He is using the Linux operating system. He wants to use a wireless sniffer to sniff the We-are-secure network. Which of the following tools will he use to accomplish his task?
- A. NetStumbler
- B. Snadboy's Revelation
- C. WEPCrack
- D. Kismet
Answer: D
NEW QUESTION 6
Which of the following is the second half of the LAN manager Hash?
- A. 0xAAD3B435B51404BB
- B. 0xAAD3B435B51404CC
- C. 0xAAD3B435B51404EE
- D. 0xAAD3B435B51404AA
Answer: C
NEW QUESTION 7
Which of the following best explains why you would warn to clear browser slate (history. cache, and cookies) between examinations of web servers when you've been trapping and altering values with a non-transparent proxy?
- A. Values trapped and stored in the browser will reveal the techniques you've used toexamine the web server
- B. Trapping and changing response values is beneficial for web site testing but usingthe same cached values in your browser will prevent you from being able to changethose value
- C. Trapping and changing response values is beneficial for web site testing but willcause browser instability if not cleare
- D. Values trapped and changed in the proxy, such as a cookie, will be stored by thebrowser and may impact further testin
Answer: D
NEW QUESTION 8
You work as a Network Security Analyzer. You got a suspicious email while working on a forensic project. Now, you want to know the IP address of the sender so that you can analyze various information such as the actual location, domain information, operating system being used, contact information, etc. of the email sender with the help of various tools and resources. You also want to check whether this email is fake or real. You know that analysis of email headers is a good starting point in such cases. The email header of the suspicious email is given below: 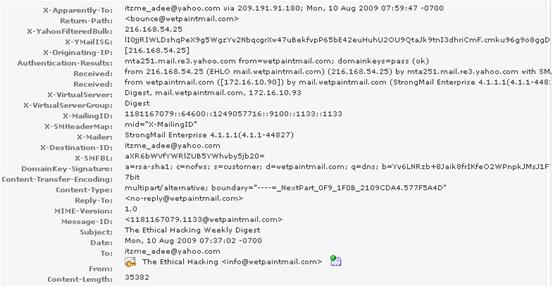
What is the IP address of the sender of this email?
- A. 172.16.10.90
- B. 209.191.91.180
- C. 141.1.1.1
- D. 216.168.54.25
Answer: D
NEW QUESTION 9
Which of the following tools uses exploits to break into remote operating systems?
- A. Nessus
- B. Metasploit framework
- C. Nmap
- D. John the Ripper
Answer: B
NEW QUESTION 10
You want to run the nmap command that includes the host specification of 202.176.56-57.*. How many hosts will you scan?
- A. 1024
- B. 256
- C. 512
- D. 64
Answer: C
NEW QUESTION 11
Analyze the command output below. Given this information, which is the appropriate next step for the tester?
Starting Nmap4.53 (hnp://insecure.org I at2010-09-30 19:13 EDT interesting ports on 192.163.116.101:
PORT STATE SERVICE
130/tcp filtered cisco-fna
131/tcp filtered cisco-tna
132/tcp filtered cisco-sys
133/tcp filtered statsrv
134/tcp filtered Ingres-net
135/tcp filtered msrpc
136/tcp filtered profile
137/tcp filtered netbios-ns
138/tcp filtered netbios-dgm
139/tcp open netbios-ssn
140/tcp filtered emfis-data
MAC Address: 00:30:1&:B8:14:8B (Shuttle)
warning: OSS can results may be unreliable because we could not find at least l open and l closed port
Device type, general purpose
Running: Microsoft Windows XP
OS details: Microsoft Windows XP SP2
Network Distance : 1 hop
Nmap done: I IP address (I host up) scanned in l .263 seconds
- A. Determine the MAC address of the scanned hos
- B. Send a single SYN packet to port 139/tcp on the hos
- C. Send spoofed packets to attempt to evade any firewall
- D. Request a list of shares from the scanned hos
Answer: B
NEW QUESTION 12
The employees of EWS Inc. require remote access to the company's Web servers. In order to provide solid wireless security, the company uses EAP-TLS as the authentication protocol. Which of the following statements are true about EAP-TLS?
Each correct answer represents a complete solution. Choose all that apply.
- A. It is supported by all manufacturers of wireless LAN hardware and softwar
- B. It uses a public key certificate for server authenticatio
- C. It uses password hash for client authenticatio
- D. It provides a moderate level of securit
Answer: AB
NEW QUESTION 13
Which of the following is the correct syntax to create a null session?
- A. c:\>net view \\IP_addr\IPC$ "" /u: ""
- B. c:\>net view \\IPC$\IP_addr "" /u: ""
- C. c:\>net use \\IP_addr\IPC$ "" /u: ""
- D. c:\>net use \\IPC$\IP_addr "" /u: ""
Answer: C
NEW QUESTION 14
Which of the following techniques are NOT used to perform active OS fingerprinting?
Each correct answer represents a complete solution. Choose all that apply.
- A. ICMP error message quoting
- B. Analyzing email headers
- C. Sniffing and analyzing packets
- D. Sending FIN packets to open ports on the remote system
Answer: BC
NEW QUESTION 15
You've been contracted by the owner of a secure facility to try and break into their office in the middle of the night. Your client requested photographs of any sensitive information found as proof of your accomplishments. The job you've been hired to perform is an example of what practice?
- A. Penetration Testing
- B. Ethical Hacking
- C. Vulnerability Assessing
- D. Security Auditing
Answer: B
NEW QUESTION 16
......
Thanks for reading the newest GPEN exam dumps! We recommend you to try the PREMIUM Surepassexam GPEN dumps in VCE and PDF here: https://www.surepassexam.com/GPEN-exam-dumps.html (385 Q&As Dumps)