It is impossible to pass CompTIA CS0-001 exam without any help in the short term. Come to Testking soon and find the most advanced, correct and guaranteed CompTIA CS0-001 practice questions. You will get a surprising result by our Far out CompTIA CSA+ Certification Exam practice guides.
Online CS0-001 free questions and answers of New Version:
NEW QUESTION 1
A cybersecurity analyst was asked to discover the hardware address of 30 networked assets. From a command line, which of the following tools would be used to provide ARP scanning and reflects the MOST efficient method for accomplishing the task?
- A. nmap
- B. tracert
- C. ping –a
- D. nslookup
Answer: A
Explanation:
Reference
https://serverfault.com/questions/10590/how-to-get-a-list-of-all-ip-addresses-and-ideally-device-names-on-a-lan
NEW QUESTION 2
A company has implemented WPA2, a 20-character minimum for the WiFi passphrase. and a new WiFi passphrase every 30 days, and has disabled SSID broadcast on all wireless access points. Which of the following is the company trying to mitigate?
- A. Downgrade attacks
- B. Rainbow tables
- C. SSL pinning
- D. Forced deauthentication
Answer: A
NEW QUESTION 3
A common mobile device vulnerability has made unauthorized modifications to a device. The device owner removes the vendor/carrier provided limitations on the mobile device. This is also known as:
- A. jailbreaking.
- B. cracking.
- C. hashing.
- D. fuzzing.
Answer: A
NEW QUESTION 4
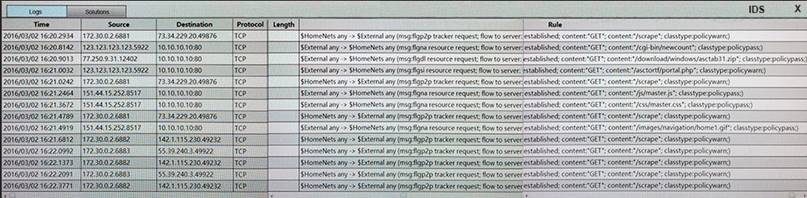
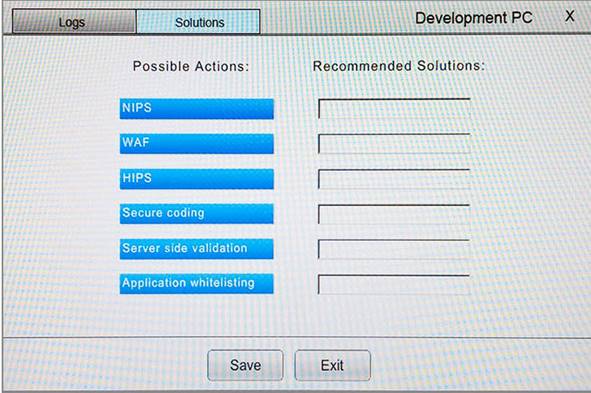
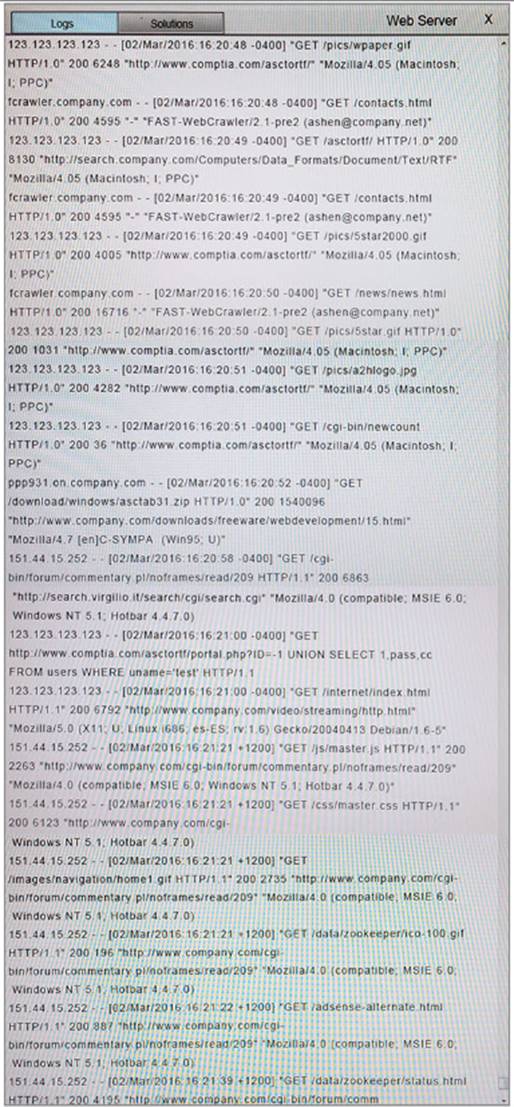
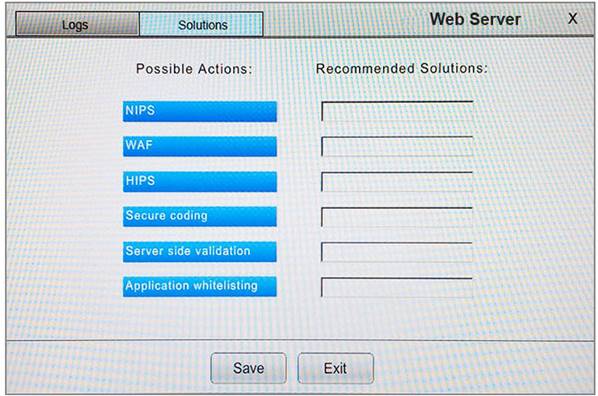
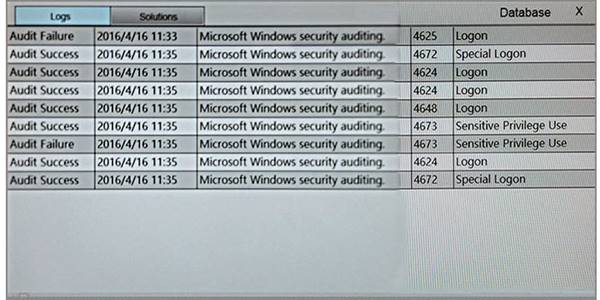
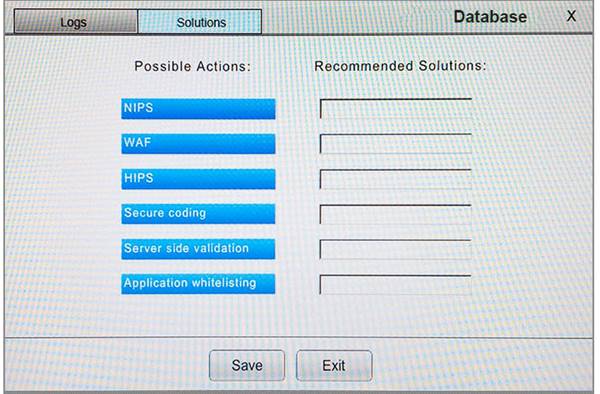
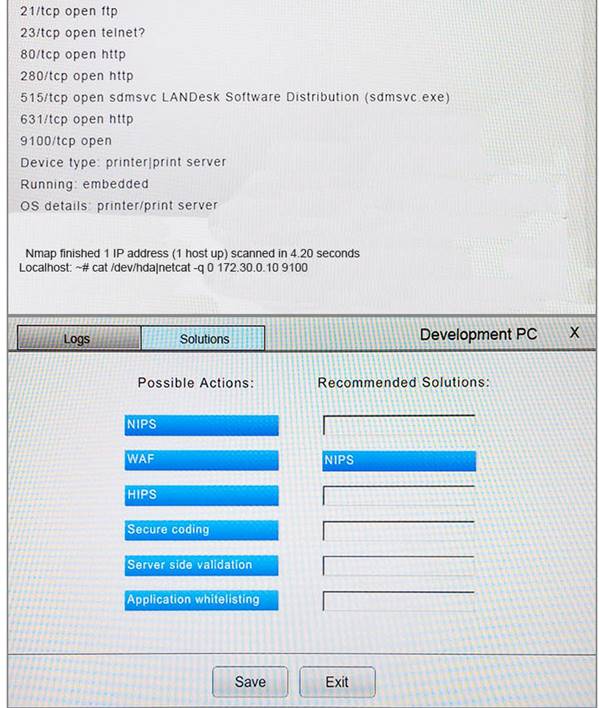
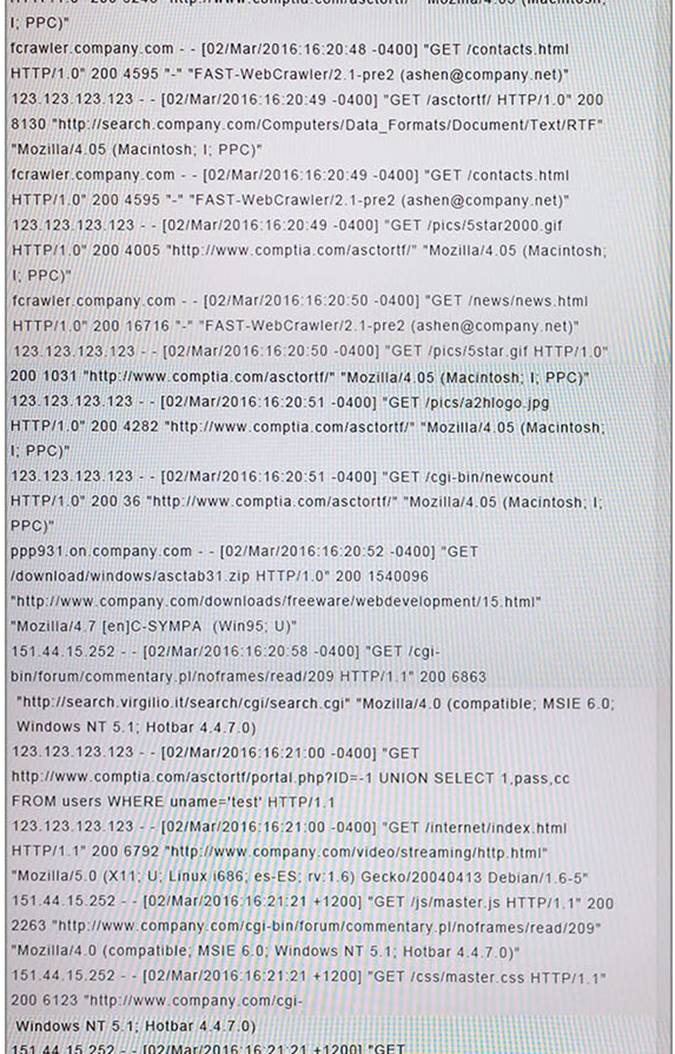
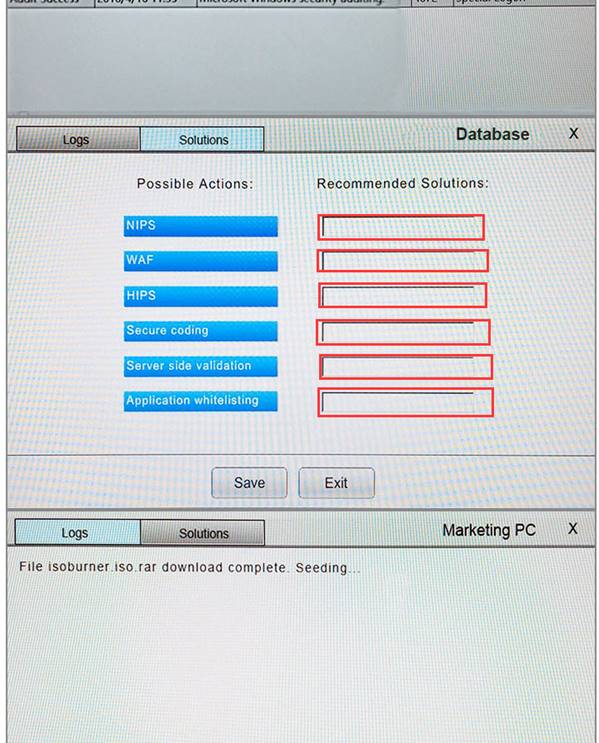
You suspect that multiple unrelated security events have occurred on several nodes on a corporate network. You must review all logs and correlate events when necessary to discover each security event by clicking on each node. Only select corrective actions if the logs shown a security event that needs remediation. Drag and drop the appropriate corrective actions to mitigate the specific security event occurring on each affected device.
Instructions:
The Web Server, Database Server, IDS, Development PC, Accounting PC and Marketing PC are clickable. Some actions may not be required and each actions can only be used once per node. The corrective action order is not important. If at any time you would like to bring back the initial state of the simulation, please select the Reset button. When you have completed the simulation, please select the Done button to submit. Once the simulation is submitted, please select the Next button to continue.






- A. Mastered
- B. Not Mastered
Answer: A
Explanation: 



NEW QUESTION 5
Management is concerned with administrator access from outside the network to a key server in the company. Specifically, firewall rules allow access to the server from anywhere in the company. Which of the following would be an effective solution?
- A. Honeypot
- B. Jump box
- C. Server hardening
- D. Anti-malware
Answer: B
NEW QUESTION 6
Given a packet capture of the following scan: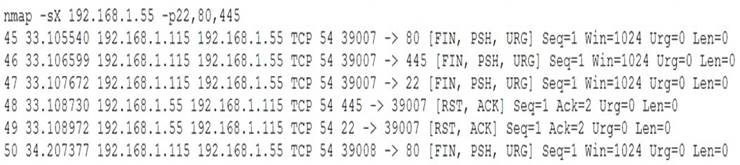
Which of the following should MOST likely be inferred on the scan’s output?
- A. 192.168.1.115 is hosting a web server.
- B. 192.168.1.55 is hosting a web server.
- C. 192.168.1.55 is a Linux server.
- D. 192.168.1.55 is a file server.
Answer: D
NEW QUESTION 7
A worm was detected on multiple PCs within the remote office. The security analyst recommended that the remote office be blocked from the corporate network during the incident response. Which of the following processes BEST describes this recommendation?
- A. Logical isolation of the remote office
- B. Sanitization of the network environment
- C. Segmentation of the network
- D. Secure disposal of affected systems
Answer: A
NEW QUESTION 8
Creating a lessons learned report following an incident will help an analyst to communicate which of the following information? (Select TWO)
- A. Root cause analysis of the incident and the impact it had on the organization
- B. Outline of the detailed reverse engineering steps for management to review
- C. Performance data from the impacted servers and endpoints to report to management
- D. Enhancements to the policies and practices that will improve business responses
- E. List of IP addresses, applications, and assets
Answer: AD
NEW QUESTION 9
After an internal audit, it was determined that administrative logins need to use multifactor authentication or a 15-character key with complexity enabled. Which of the following policies should be updates to reflect this change? (Choose two.)
- A. Data ownership policy
- B. Password policy
- C. Data classification policy
- D. Data retention policy
- E. Acceptable use policy
- F. Account management policy
Answer: BF
NEW QUESTION 10
A network technician is concerned that an attacker is attempting to penetrate the network, and wants to set a rule on the firewall to prevent the attacker from learning which IP addresses are valid on the network. Which of the following protocols needs to be denied?
- A. TCP
- B. SMTP
- C. ICMP
- D. ARP
Answer: C
NEW QUESTION 11
A security analyst is preparing for the company's upcoming audit Upon review of the company's latest vulnerability scan, the security analyst finds the following open issues:
Which of the following vulnerabilities should be prioritized for remediation FIRST?
- A. ICMP timestamp request remote date disclosure
- B. Anonymous FTP enabled
- C. Unsupported web server detection
- D. Microsoft Windows SMB service enumeration via srvsvc
Answer: C
NEW QUESTION 12
A technician is running an intensive vulnerability scan to detect which ports are open to exploit. During the scan, several network services are disabled and production is affected. Which of the following sources would be used to evaluate which network service was interrupted?
- A. Syslog
- B. Network mapping
- C. Firewall logs
- D. NIDS
Answer: A
NEW QUESTION 13
A security analyst has discovered that an outbound SFTP process is occurring at the same time of day for the past several days. At the time this was discovered large amounts of business critical data delivered. The authentication for this process occurred using a service account with proper credentials. The security analyst investigated the destination IP for (his transfer and discovered that this new process s not documented in the change management log. Which of the following would be the BESST course of action for the analyst to take?
- A. Investigate a potential incident
- B. Verify user per missions
- C. Run a vulnerability scan
- D. Verify SLA with cloud provider
Answer: A
NEW QUESTION 14
Following a recent security breach, a post-mortem was done to analyze the driving factors behind the breach. The cybersecurity analysis discussed potential impacts, mitigations, and remediations based on current events and emerging threat vectors tailored to specific stakeholders. Which of the following is this considered to be?
- A. Threat intelligence
- B. Threat information
- C. Threat data
- D. Advanced persistent threats
Answer: A
NEW QUESTION 15
Datacenter access is controlled with proximity badges that record all entries and exits from the datacenter.
The access records are used to identify which staff members accessed the data center in the event of equipment theft.
Which of the following MUST be prevented in order for this policy to be effective?
- A. Password reuse
- B. Phishing
- C. Social engineering
- D. Tailgating
Answer: D
NEW QUESTION 16
A cybersecurity consultant found common vulnerabilities across the Mowing, services used by multiple severs at an organization: VPN. SSH, and Ml I PS. Which of the following is the MOST likely reason for the discovered vulnerabilities?
- A. Leaked PKI private key
- B. Vulnerable version of OpenSSL
- C. Common initialization vector
- D. Weak level of encryption entropy
- E. Vulnerable implementation of PEAP
Answer: D
NEW QUESTION 17
During a review of security controls, an analyst was able to connect to an external, unsecured FTP server from a workstation. The analyst was troubleshooting and reviewed the ACLs of the segment firewall the workstation is connected to:
Based on the ACLs above, which of the following explains why the analyst was able to connect to the FTP server?
- A. FTP was explicitly allowed in Seq 8 of the ACL.
- B. FTP was allowed in Seq 10 of the ACL.
- C. FTP was allowed as being included in Seq 3 and Seq 4 of the ACL.
- D. FTP was allowed as being outbound from Seq 9 of the ACL.
Answer: A
NEW QUESTION 18
A cybersecurity analyst is reviewing the following outputs: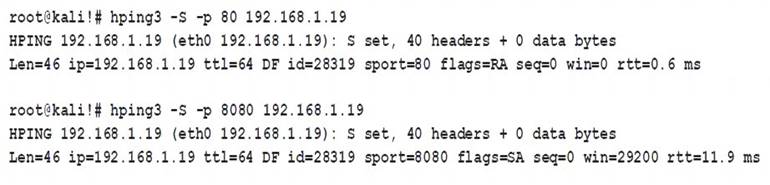
Which of the following can the analyst infer from the above output?
- A. The remote host is redirecting port 80 to port 8080.
- B. The remote host is running a service on port 8080.
- C. The remote host’s firewall is dropping packets for port 80.
- D. The remote host is running a web server on port 80.
Answer: B
NEW QUESTION 19
An organization wants to remediate vulnerabilities associated with its web servers. An initial vulnerability scan has been performed, and analysts are reviewing the results. Before starling any remediation the analysts want to remove false positives to avoid spending time on issues that are not actual vulnerabilities. Which of the following would be an indicator of a likely false positive?
- A. Reports indicate that findings are informational.
- B. Any item& labeled "low" are considered informational only.
- C. The scan result version is different front the automated asset inventory.
- D. HTTPS entries indicate the web page is encrypted securely.
Answer: A
NEW QUESTION 20
Which of the following actions should occur to address any open issues while closing an incident involving various departments within the network?
- A. Incident response plan
- B. Lessons learned report
- C. Reverse engineering process
- D. Chain of custody documentation
Answer: B
NEW QUESTION 21
A security analyst is reviewing a report from the networking department that describes an increase in network utilization, which is causing network performance issues on some systems. A top talkers report over a
five-minute sample is included.
Given the above output of the sample, which of the following should the security analyst accomplish FIRST to help track down the performance issues?
- A. Perform reverse lookups on each of the IP addresses listed to help determine if the traffic necessary.
- B. Recommend that networking block the unneeded protocols such as Quicklime lo clear up some of the congestion
- C. Put ACLs in place to restrict traffic destined for random or non-default application ports
- D. Quarantine the top talker on the network and begin to investigate any potential threats caused by the excessive traffic
Answer: A
NEW QUESTION 22
A malware infection spread to numerous workstations within the marketing department. The workstations were quarantined and replaced with machines.
Which of the following represents a FINAL step in the eradication of the malware?
- A. The workstations should be isolated from the network.
- B. The workstations should be donated for reuse.
- C. The workstations should be reimaged.
- D. The workstations should be patched and scanned.
Answer: D
NEW QUESTION 23
A security audit revealed that port 389 has been used instead of 636 when connecting to LDAP for the authentication of users. The remediation recommended by the audit was to switch the port to 636 wherever technically possible. Which of the following is the BEST response?
- A. Correct the audi
- B. This finding is a well-known false positive; the services that typically run on 389 and 636 are identical.
- C. Change all devices and servers that support it to 636, as encrypted services run by default on 636.
- D. Change all devices and servers that support it to 636, as 389 is a reserved port that requires root access and can expose the server to privilege escalation attacks.
- E. Correct the audi
- F. This finding is accurate, but the correct remediation is to update encryption keys on each of the servers to match port 636.
Answer: B
NEW QUESTION 24
The help desk informed a security analyst of a trend that is beginning to develop regarding a suspicious email that has been reported by multiple users. The analyst has determined the email includes an attachment named invoice.zip that contains the following files:
Locky.js xerty.ini xerty.lib
Further analysis indicates that when the .zip file is opened, it is installing a new version of ransomware on the devices. Which of the following should be done FIRST to prevent data on the company NAS from being encrypted by infected devices?
- A. Disable access to the company VPN.
- B. Move the files from the NAS to a cloud-based storage solution.
- C. Set permissions on file shares to read-only.
- D. Add the URL included in the .js file to the company’s web proxy filter.
Answer: D
NEW QUESTION 25
A centralized tool for organization security events and managing their response and resolution is known as:
- A. SIEM
- B. HIPS
- C. Syslog
- D. Wireshark
Answer: A
NEW QUESTION 26
A systems administrator is trying to secure a critical system. The administrator has placed the system behind a firewall, enabled strong authentication, and required all administrators of this system to attend mandatory training.
Which of the following BEST describes the control being implemented?
- A. Audit remediation
- B. Defense in depth
- C. Access control
- D. Multifactor authentication
Answer: B
NEW QUESTION 27
Various devices are connecting and authenticating to a single evil twin within the network. Which of the following are MOST likely being targeted?
- A. Mobile devices
- B. All endpoints
- C. VPNs
- D. Network infrastructure
- E. Wired SCADA devices
Answer: A
Explanation:
Reference
http://www.corecom.com/external/livesecurity/eviltwin1.htm
NEW QUESTION 28
A security analyst reserved several service tickets reporting that a company storefront website is not accessible
by internal domain users. However, external users ate accessing the website without issue. Which of the following is the MOST likely reason for this behavior?
- A. The FQDN is incorrect.
- B. The DNS server is corrupted.
- C. The time synchronization server is corrupted.
- D. The certificate is expired.
Answer: B
NEW QUESTION 29
A security analyst is reviewing packet captures for a specific server that is suspected of containing malware and discovers the following packets:
Which of the following traffic patterns or data would be MOST concerning to the security analyst?
- A. Ports used for SMTP traffic from 73.252.34.101
- B. Unencrypted password sent from 103.34.243.12
- C. Anonymous access granted by 103.34.243.12
- D. Ports used HTTP traffic from 202.53.245.78
Answer: C
NEW QUESTION 30
A security analyst has noticed an alert from the SIEM. A workstation is repeatedly trying to connect to port 445 of a file server on the production network. All of the attempts are made with invalid credentials. Which of the following describes what is occurring?
- A. Malware has infected the workstation and is beaconing out to the specific IP address of the file server.
- B. The file server is attempting to transfer malware to the workstation via SMB.
- C. An attacker has gained control of the workstation and is attempting to pivot to the file server by creating an SMB session.
- D. An attacker has gained control of the workstation and is port scanning the network.
Answer: C
NEW QUESTION 31
......
Recommend!! Get the Full CS0-001 dumps in VCE and PDF From Simply pass, Welcome to Download: https://www.simply-pass.com/CompTIA-exam/CS0-001-dumps.html (New 363 Q&As Version)